An announced vendor policy is not a law
Anthropic published a new Usage Policy on October 8 and said the update takes effect on November 12. The announcement says much of the revision clarifies existing rules, adds examples for longer, more independent work, and updates provisions concerning high-risk uses and autonomous physical actions. It also describes a human-review requirement for certain uses that can affect health, legal rights, finances, livelihood, or essential services.
Those are Anthropic’s product rules, not a statement of what the law requires in every jurisdiction. A customer still needs to check applicable contracts, local law, and internal policy. The useful operational task is to identify which workflows use the service, what the policy says about them, and who can make a change before the effective date.
Inventory actual workflows, not labels
Search for workflows that use Claude or a connected service, then record the user, purpose, data, model surface, tools, and downstream action. ‘Customer support’ or ‘research’ is too broad to evaluate. A workflow that drafts an answer for review differs from one that decides which person receives a service or triggers an external action.
Include low-visibility uses such as scheduled runs, shared prompts, embedded assistants, and API calls in another product. Ask each owner to identify the affected person, the decision being supported, the reviewer, and the point at which a human can change the result. This reveals policy questions that a list of approved tools alone will miss.
Map each policy change to a control
For every relevant use case, cite the specific policy section, summarize the practical requirement, and record the control that meets it. If the policy requires a qualified reviewer for a high-impact recommendation, name the person with authority to revise or reject it. If an automated action is connected to hardware, identify the operator and the safe state the system can hold if disconnected.
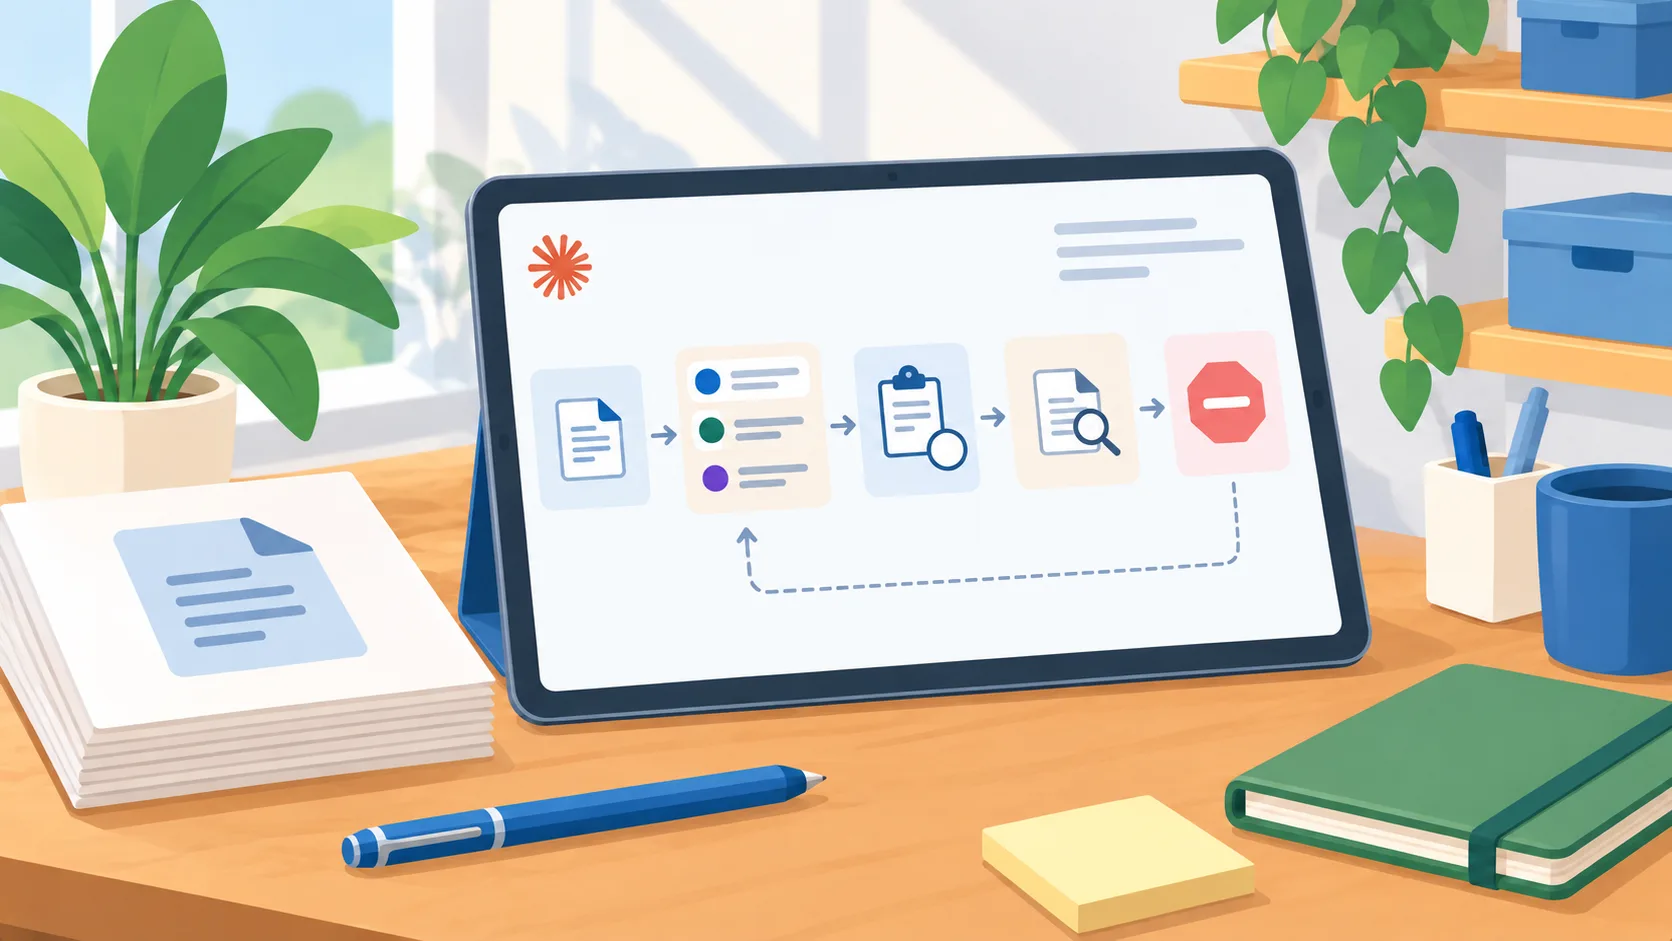
Do not claim that a process is compliant merely because a reviewer exists in the diagram. Test whether the reviewer sees the evidence, has enough time, and can block the action before it takes effect. Keep records of overrides and unresolved exceptions so a policy review can examine behavior rather than a paper description.
Give owners a focused readiness checklist
Ask workflow owners to confirm their purpose, data class, user notice, human authority, output destination, and fallback. Have security review access and logging; have legal or policy staff interpret obligations; have operations validate the stop path. This is a focused change review, not a blanket suspension of all AI work.
If a workflow has no clear owner or the policy mapping is uncertain, pause new expansion until someone accepts responsibility. Keep the existing process available and explain the reason for any hold. A short written exception should identify the question, the person who will resolve it, and the date when the decision will be revisited.
What to do before November 12
Use the remaining review period to inspect the official policy and current supported-region rules, then test the mapped controls in a staging or low-risk workflow. Preserve a copy of the version you reviewed and the internal decision, since vendor policies can change. Do not rely on a summary page alone when the full rule is available.
The practical outcome should be a small record for each workflow: keep as designed, add a control, narrow the use, or stop it. This creates a traceable decision without confusing a vendor’s terms with law or a general announcement with an individual legal conclusion. If the consequence is material, ask qualified counsel to review the actual use and jurisdiction.